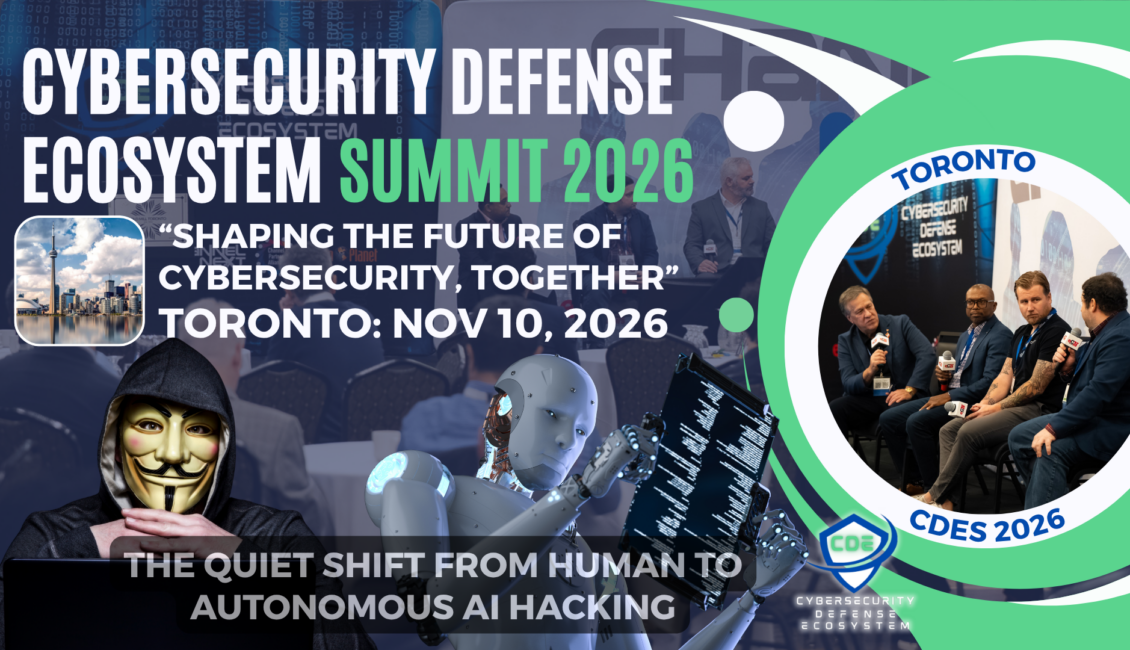
Cybersecurity Defense Ecosystem Summit 2026 – Canada

“Shaping the Future of Cybersecurity in Canada, Together”

If you are an MSP, MSSP, SOC, CISO or a Cybersecurity Professionals, then this event, community and resource is for you to learn, network and improve your cyber practice.

Keynote by Ross Young: From CIA spy to CISO “Why Most Cyber Budgets Go To Waste”

“In the absence of a cohesive team strategy for cybersecurity, malicious actors will continue to succeed and now with autonomous AI Agents, they will succeed much faster”

The Cybersecurity Defense Ecosystem Summit (CDES) is inviting ALL cybersecurity stakeholders to unite for networking, learning, and collaboration. With 90% of content delivered through panel discussions, experts and peer-to-peer collaborations you get the widest perspectives and exchange of unbiased ideas!

The Quiet Shift from Human to Autonomous AI Hacking is here. Are you ready to defend tomorrow?

Forget about cyber fear-mongering, AI doom-and-gloom, or boring product pitches—we have all had more than enough of that. Instead, this event focuses on practical, sensible strategies to protect against cyber threats without exhausting your budget or burning out your team.

Join us to evaluate your current security posture—the good, the bad, and the ugly—and discover how to enhance protection while keeping costs down (or even cutting them). Rather than adding more tools, it is time to move toward smart, effective cybersecurity.

Several key trends are currently converging that impacts cybersecurity: the rise of autonomous AI agent hacking, advanced LLM capabilities with AGI enhancements, and the consolidation of platforms and solutions driven by AI. Furthermore, the industry faces significant expansion of regulations and the ongoing challenge of a workforce utilizing more shadow AI and IT. Understanding your risk landscape to better protect, FAST and efficient detection of threats, rapid intervention and mediation are all mission critical.

Left of Boom: Our expert panel will analyze emerging trends in Autonomous AI Agent Hacking and discuss robust and smart defensive strategies. As the next generation of AI evolves into a sophisticated cyber weapon, it grants advanced hacking capabilities to a broader range of actors and enables relentless, autonomous attacks. This shift fundamentally alters the “Left of Boom” landscape, making rapid detection and remediation the new mission-critical standard. We will examine how leveraging intelligent AI automation and tool consolidation can reduce cybersecurity expenditures while improving your overall risk profile. Additionally, we will explore maintaining a resilient security posture through continuous AI-powered monitoring and the implementation of smarter patch management and configuration strategies.

Right of Boom: From detection to recovery, we will examine the most recent advancements in continuous, always-on penetration testing designed to identify and close critical gaps. Being prepared is essential; therefore, we will discuss practical Table Top Exercises and introduce an Incident Response Platform to manage the process. This platform serves as a powerful tool for detecting, halting, and mediating breaches as they happen. Surviving a cyber incident is a notoriously difficult experience, yet organizations can improve their outcomes by equipping themselves with the necessary tools, information, and expertise. Key strategies include:

  • Real-Time Visibility: Understanding exactly which data has been compromised in real-time allows for more informed recovery decisions.
  • Diligent Practice: Regular incident response drills reduce panic, alleviate stress, and prevent expensive errors during a crisis.
  • Financial Protection: We will explore methods for securing affordable cyber insurance to ensure an expert team of responders can be deployed immediately if primary defences fail.

Consistent IR practice combined with a solid cyber insurance policy remains the most effective way in ensuring a business can survive following a cyberattack.

Did you know that the top 20 vendors—out of 6,000—account for 66% of global cybersecurity spending, yet they still face attacks and breaches. Meanwhile, thousands of smaller vendors are working to fill the gaps. Everyone has a role to play and AI will help, but cost and skill shortages remain major challenges. Data sovereignty, compliance, and other regulations are forcing a rethink of cybersecurity strategies.

Even as AI fuels the ongoing “Cyber War,” human involvement remains crucial. This event will explore the latest AI landscape, the evolution of Identity Management to Autonomous Agents, and emerging quantum computing technologies.

  • Managed Security Services Providers (MSSPs)
  • Cybersecurity-First MSPs
  • Security Operations Centres (SOCs)
  • Chief Information Security Officers (CISOs)
  • Chief Information Officers (CIOs)
  • Cybersecurity Consultants
  • Vendors developing cybersecurity solutions or offering services
  • AI Consultants
  • Business owners and C-suite executives seeking to understand cyber breach risks.
  1. Practical Cyber Discussions: Delve into the latest cybersecurity challenges, particularly from an AI perspective, and explore mediation strategies.
  2. Community Building: Cybersecurity is a team sport. This event fosters a network of top regional cyber experts for year-round collaboration against cybercrime, extending beyond a one-time gathering.
  3. Latest Technologies: Experience cutting-edge cyber technologies and resilience practices, including advancements in AI and identity management, to protect businesses effectively.
  4. Left and Right of Boom: Learn to prevent breaches with the strategies while preparing for the “Boom” (a breach) with insights on detection, response, recovery, and reporting.
  5. CISO Challenges: Engage in discussions about CISO challenges with C-Level management and explore how MSPs and MSSPs can collaborate with CISOs and CIOs to enhance cybersecurity posture.
  6. Growing Impact of AI on Cyber: Explore how AI is transforming cybersecurity and its future implications. Discussions will also cover the business use of AI and the significant risks without proper governance and policies.
  7. Compliance and Regulations: Gain understanding of government and insurance compliance requirements (reporting, privacy laws) and strategies for a defendable legal position, including cyber insurance.
  8. Assessing Cyber Risks: Understand your cyber risk profile and learn to evaluate your security posture to your desired level.
  9. Supply Chain Protection: Discover strategies to safeguard the supply chain and address emerging threats like non-human identities, software code, web, and eCommerce vulnerabilities.
  10. Open Town Hall Discussion: Participate in meaningful discussions and debates with the audience

Keep watching for updates and previews as we get closer!

Balancing Affordability with Cybersecurity Protection:

Small to Mid-Size Businesses: The cost of cybersecurity continues to rise, making it challenging for SMBs to balance protection with budget. Tech-sprawl and overlapping functionality complicate solution adoption. The summit will also offer insights on minimizing costs through consolidation, tech stack analysis and AI automation, potentially reducing cyber risks while minimizing costs.

Ticket Prices:

Make the Cybersecurity Defense Ecosystem your new go-to home and local community for all things cyber. MSPs, MSSPs, SOCs, and CISOs can sign up for free and start exploring today with a Basic Free Membership and get an additional $100 discount to attend this summit.

$248 (Plus Ticket Provider Handling and Taxes) Get $100 extra discount as a CDE Member!

NOTE: If you are already a CDE member, you will receive a discount code by email. If you did not, please contact us at the CDE. For new members, please sign up first to the CDE first then check your email for the special discount code, then use that to register online.

Explore the CDE: A Resource for those in the business of cybersecurity. MSPs, MSSPs, SOCs, CISOs and Vendors.

Event Details
Free CDE Membership = $100 discount to CDE Summit

This in-person event is the premier gathering for the Cybersecurity Defense Ecosystem (CDE) community, bringing together cybersecurity professionals, makers, buyers, and sellers. It's a unique opportunity to learn, network, and collaborate. Members can connect face-to-face and exchange ideas, while non-members can experience the CDE firsthand and engage with its influential network of experts.

While the chance to network and share insights among peers is valuable in itself, this event offers much more. Attendees will hear from top minds in cybersecurity. Whether you're a seasoned expert or just beginning to deepen your cybersecurity capabilities, this event is designed to deliver significant value.

Experience it for yourself and decide. We are hosting several events across the country, and you are welcome to join any of them.

Agenda

We officially kick off at 9:00 AM, but feel free to arrive as early as 8:00 AM to enjoy breakfast snacks, fresh coffee, and some valuable time to meet, greet and network with peers, speakers and experts.

Stronger Together. Year-Round.

Build powerful connections, share insights, and grow your business at our cybersecurity summit. With the Cybersecurity Defense Ecosystem, you get 24/7 access to tools, expertise, and a network of leaders to boost your security protection.

Join free at cybersecuritydefenseecosystem.com or unlock premium benefits for $595/year.

These regional CDE summits unite MSPs, MSSPs, SOCs, and CISOs to network, learn, and collaborate—driving cybersecurity excellence all year long.

Ross Young will deliver a high-impact keynote on what matters most in today's cybersecurity.

What you should worry about and prioritize.

He will explore some of his finding from his book "Cybersecurity's Dirty Secret: Why Most Budgets Go to Waste." to show you how to maximize cybersecurity outcomes per dollar, saving your organization thousands to millions in wasted spending.

You will learn how to: apply practical templates, tools, and frameworks immediately; determine optimal cybersecurity spending and fix boardroom ROI metrics; avoid risky budget cuts and decide when to switch, double down, or drop tools; cut IT labor costs using automation, AI, and neurodiverse talent; and eliminate budget killers like bad contracts, inefficient meetings, and accountability gaps.

It is today's playbook to make cybersecurity cost-effective, faster, and better—turning it from a cost sink into a key value driver.

That is not all!

He will tackle the latest in managing application vulnurabilities with the rise of powerful AI platforms like Mythos. He will also be part of our Town Hall discussion to answer your questions!

Come get a signed copy of his book!

To wrap this up, we will spotlight a few solutions that you can leverage to assess your current cybersecurity posture. Is it working? Is it enough? It is too much?

A live example of the latest in autonomous AI hacking to better understand how this is happening.

Before an attack is meticulously planned and carried out, a group of AI agents is dispatched by malicious actors to gather intelligence about the target company and its employees from all accessible sources, including the dark web. This information is carefully analyzed to develop an attack strategy that outlines who to target, why, where, and how.

Leveraging someone's identity and log in credentials is still the number one way hackers gain access. AI agents amplifies the identity problem.

Tactics are dynamically adjusted with the assistance of AI.

Once inside, they patiently explore to identify the most valuable data before executing their plan and retreating. Utilizing AI cloaking and various strategies, hackers can extract sensitive information or deploy malware without being detected. While some companies have measures and personnel in place to identify and prevent such incidents, the vast majority do not. With AI at their disposal, malicious actors gain an edge by automating more sophisticated and well-organized attacks.

This next level of automated Hacking-as-a-Service is available to anyone.

How can you safeguard against these types of threats? This session explains what vulnerability prioritization actually means and how MSP,MSSP and CISO teams must collaborate to prioritize what to fix first.

Cyber and fraud are no longer separate challenges, they have converged into a single, rapidly evolving threat. As cybercriminals harness artificial intelligence to scale, automate, and personalize attacks, organizations are facing an unprecedented surge in sophisticated phishing campaigns, social engineering scams and impersonation that leads to financial fraud while eroding the credibility of our organizations. In this session, we will explore how AI is reshaping the threat landscape and driving the growing convergence of cybercrime and fraud. The discussion will highlight why traditional siloed approaches are no longer sufficient and why a unified defense strategy is essential.

AI and Cybersecurity are becoming more regulated in more countries.

Failure or ignorance to comply will no longer be an option. Companies will be held liable and cyber insurance claims will be denied if your compliance posture is not defendable.

There are several components to the best Cybersecurity practice and it continues to evolve...

Compliance, CIS, regulations, privacy, insurance, supply chain, and other legal issues play a critical role in your overall cybersecurity posture.

In many cases defendable compliance is becoming a requirement to do business with an increasing number of organizations and Governments.

Today, it's vital to keep ahead of the latest government and insurance regulations (both in-country and international).

This will be a practical discussion on how Canadian organizations should choose and apply frameworks instead of turning cybersecurity into checkbox compliance.

We will also showcase some self-help tools and services to help you assess the current state of your compliance and what may be missing.

To say that cybersecurity challenges are on the rise is gross an understatement. We sill share the latest data on the current state of attacks including how deepfakes and AI agents are continuously changing the game.

Cybersecurity is a TEAM sport. No one can do it alone. In this session will be bring to gather all of the stakeholders - MSPs, MSSPs, SOCs, CISOs, CIOs and other c-suite executives to discuss how we have to balance business needs with cybersecurity risks, especially in the age of AI.

Cybersecurity is a team sport. How do you balance business needs with cyber risks? How do you balance AI with cybersecurity? How can all stakeholders find common ground to make the best decisions for growing business, protecting clients and preventing cyber breaches?

In this session, we will be bringing together all of the stake holders to explore how we can all get along and make smarter decisions.

With over 6,000 cybersecurity solutions, limited resources and budgets, how can you implement the proper cybersecurity protection to mediate your risks? This session will explore the power of multi-vendor platform consolidation and how that can deliver better protection.

With the speed of AI and autonomous hacking, it is impossible for humans to defend at machine speed. You will explore a solution that detects anomalies in real-time and mediates in real-time.

Most businesses rely on ERP to run their most critical operations and manage some of their most valuable data. In many ways, ERP sits at the center of the enterprise.

AI raises the stakes. The same data that can drive better decisions, automation, and growth also requires greater attention to security, governance, resilience, and responsible access.

So businesses should be asking a different set of questions:
Is your ERP environment prepared for today’s evolving threat landscape and the governance demands of AI-enabled workflows?
When did you last examine the security, vulnerability-management, and remediation practices supporting your ERP environment?

And how resilient is the operational data at the heart of your business?

For organizations operating ERP environments that have evolved over many years, the question is no longer simply, "Does our ERP work?”

Is it maintainable? Is it resilient? Is it governed? And is it ready for AI?

In this session, we’ll explore how modern, industry-specific cloud ERP is changing that conversation and how Infor is helping organizations in manufacturing and other industries modernize their operational foundation while addressing security, privacy, governance, and continuous innovation.

But there is another significant opportunity.

Cybersecurity firms, MSPs, MSSPs, AI and data specialists, and systems integrators already help customers secure and modernize critical parts of their technology environment. ERP represents a natural extension of that conversation.

As customers modernize their ERP environments and introduce AI into core business processes, they will need partners that can bring together business transformation, technology, data, integration, AI, and cybersecurity expertise.

That creates an opportunity for a new generation of Infor partners.

Come explore the intersection of ERP, cybersecurity, AI, and industry transformation, and why building an ERP practice around Infor can create new capabilities, customer relationships, and revenue opportunities for technology partners.

Most every company is rapidly deploying more AI. In this secession we will cover the critical requirements of AI Governance and why it matters.

We will also explore the growing risks and how to best medicate to better protect your company while leverage all of the benefits of AI.

Catch 2-minute pitches on innovative cyber solutions and services.

You'll get a high-level overview of various solutions and business tools, then vote for your favorite pitch.

Meet vendors all day—discover opportunities, spark partnerships, and open new doors.
This panel discussion will bring together various perspectives on how cybersecurity leaders are shaping the future of Canada and what we must do today. What resources we will need to defend tomorrow.

The panel will consist of:

Jon Rohrich, Avanade
Vivian Odii, IAM at RBC
Mario Alejandro Matiz Zambrano, CIBC Vulnerability Management Program
Camille Kloppenburg, Application Security at CIBC

What's on your mind? What do you want to know? What do you care about? You get to choose!

Pick your table top workshop - 15 to choose from!

Join the group interested in the specific topic. An expert on the topic will be hosting these table-top candid discussions. Whatever happens in these discussions stays confidential.
These sessions are about addressing YOUR questions. If none the listed topics fit for you, then start your own topic!

We have all the cyber experts available and ready to adjust the discussion to meet your needs.

Shadow AI and Data Leakage
Should I VIBE code my own cyber tools
Measuring ROI on your Cyber Tools
Private LLMs
LLM/AI Poisoning?
Non-Human Identity Management
PAM
RedTeam
PEN Testing
Supply Chain Security Management
Shadow IT
Human resources
Insider Threats
Awareness Training in the Era of Deepfakes
And more...

We wrap up the event in the Expo with some social networking.

After-event activities: All registered attendees will be notified of special invite-only dinners hosted by various organizations.

Typically, many end up in the hotel bar to carry on the conversations.

Please do NOT Drink and Drive! There are hotel rooms available and many car share options available. Just leave your car if you drove and arrive safe!

While we do have an official end-time, we will be around until 7 PM and everyone is welcome to continue the networking. Please do not drink and drive! There are hotel rooms available in the venue.

The CDE Resource is open all year long!

Cybersecurity is a team sport, and the landscape is constantly shifting—no single event can ever address all your needs or answer every question before the game changes again. That is why the primary mission of CDE is to help you build an ongoing personal ecosystem of peers, experts, and tools to combat cybercrime year-round.

In addition to our periodic regional gatherings, CDE empowers members to connect as often as they like by hosting virtual sessions, participating in local chapter events, or joining Mastermind Peer Groups and Pods. Join a dedicated community to stay ahead of cyber threats all year long.

Join the CDE: https://cybersecuritydefenseecosystem.com/
Cyber Peer Groups or Pods: https://www.channelpartneralliance.com/
Ask about hosting local CDE Chapters!

Registration
$248 (CDE Members get $100 Additional Discount, so only $148)
248

Taxes and Ticket Platform Handling Fees Extra.
Ticket Includes:

Full event access
Breakfast
Lunch

FAQ

What topics are planned to be covered at the event?

1. Cybersecurity in the Age of AI Agents
A short opening talk framing how cybersecurity has shifted from AI awareness to AI execution, with AI agents, identity, data access, and automation now becoming real operational risks.

2. Frameworks
A practical discussion on how organizations should choose and apply frameworks without turning cybersecurity into checkbox compliance.

3. Vulnerability Prioritization in the Era of AI
What vulnerability prioritization actually means, why CVSS alone is not enough, and how teams should decide what to fix first.

4. Defense in Depth in the Era of AI
A modern look at layered defense across identity, email, endpoint, cloud, SaaS, data, AI agents, backups, and human behavior.

5. AI Pen Testing Lessons Learned
What breaks when testing AI applications, copilots, RAG systems, chatbots, and internal AI agents, and what organizations can do before production use.

6. The Rise of the CISO: AI Governance, Risk, and Board Communication
How security leaders explain AI risk, cyber investment, resilience, and business impact to executives and boards.

7. From Reactive to Predictive to Agentic Defense
A continuation of the AI defense conversation, moving from reactive security to predictive detection and safe AI-assisted response.

8. Identity Is No Longer Just About People
Human users, service accounts, APIs, bots, non-human identities, and AI agents that now need stronger governance and access control.

9. Shadow AI and Data Leakage
How employees are already using AI tools, where sensitive data may be leaking, and how companies can manage it without blocking innovation.

10. Ransomware 2026: Faster, Smarter, More Automated
A threat landscape update focused on ransomware, identity abuse, social engineering, and the operational gaps attackers continue to exploit.

11. Software Supply Chain and Third-Party Risk
How organizations can understand exposure across vendors, software components, SaaS tools, and critical third parties.

12. Cyber Insurance, Compliance, and Contracts
How cyber maturity now affects insurance, customer trust, procurement, and contract requirements.

13. Security Awareness in the Age of Deepfakes and AI Phishing
How awareness training must evolve when attackers can generate better phishing, voice cloning, deepfakes, and personalized scams.

14. Cyber Resilience: Recovery Is the New Differentiator
Backups, incident response, tabletop exercises, business continuity, and proving the organization can recover after an attack.

15. Vendor Proof, Not Vendor Promises
A sharper vendor pitch format where each vendor must explain the risk they solve, the proof they have, and the business outcome they deliver.

16. CISO Court: Put the Security Claim on Trial
The CISOs challenge on vendor claim, framework idea, or security assumption to test what is real, useful, and measurable.

17. AI Governance for MSPs and MSSPs
How MSPs and MSSPs can help customers adopt AI securely and turn AI security into a service opportunity.

18. What Can Be Done Now: 30/60/90-Day Cyber Action Plan
A closing action plan where experts give clear actions attendees can take immediately, within 60 days, and within 90 days.

Where is the CDES held?

At the Old Mill, 9 Old Mill Rd, Etobicoke, ON M8X 1G5, Canada. Parking is available. Nearby access by subway.

How to get there?

There is a subway station at walking distance. There is ample parking by the venue. Website: https://www.oldmilltoronto.com/

How do I become a Member to the Cybersecurity Defense Ecosystem (CDE) for FREE and attend the event with a $100 discount?

It's simply - ONLY if you are an MSP, MSSP, SOC, CISO, CIO or Cybersecurity Consultant, sign up at https://cybersecuritydefenseecosystem.com/channel-partner-sign-up/

Membership in the CDE allows you to access a comprehensive cybersecurity resource all year long. Explore the benefits and if you want to unlock much more benefits, become Premium Member for $595 USD per year. No obligation to renew. To renew for the next year(s), you must complete the renewal process and payment at or before end of the first year.

When should I arrive?

Plan to arrive by 8:00 AM to network with everyone over breakfast snacks and coffee.

The sessions start at 9:00 AM.

How do I participate if I do not want to become a CDE member?

You can purchase a ticket for $495.00. Ask for an Executive Overview if you need to justify the expenditure by your company.

If I am a vendor and do not exhibit, how can I attend?

Buy a ticket for $495. Vendors cannot become a member of the CDE. If you wish to exhibit, please ask for the sponsorship options and exec summary.

Contact us if you have other questions https://www.channelnext.ca/contact/

Gallery

For more pictures from previous CDE Summits, please check out this website.

Photos
Eric_Parent
Event Details
Sponsors
Share on social media