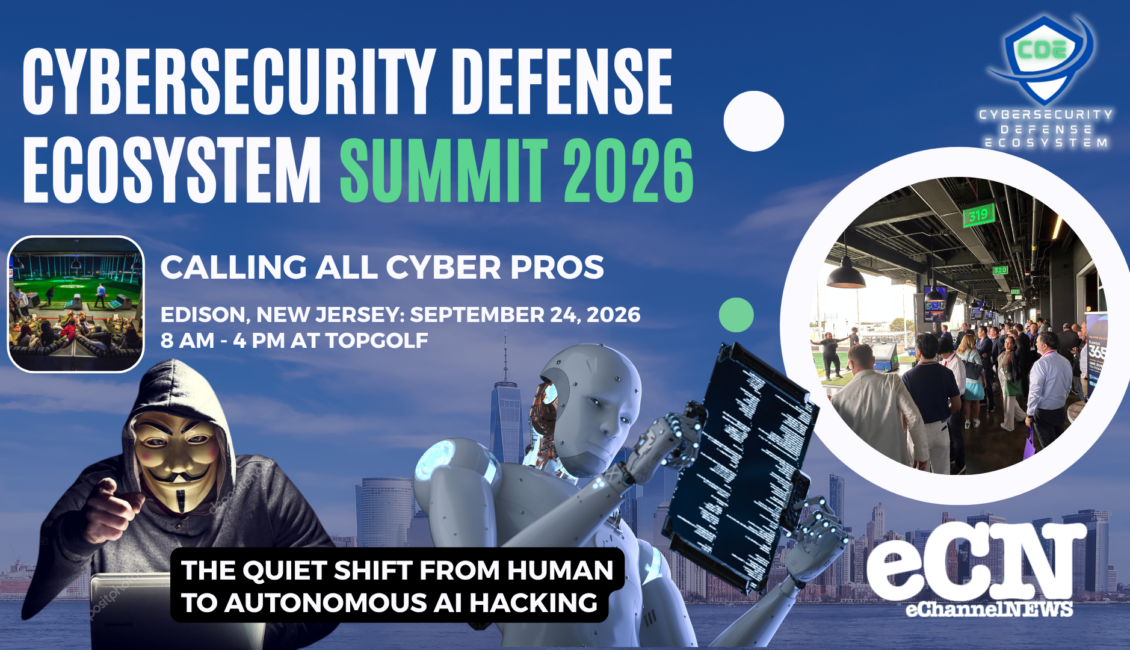
Cybersecurity Defense Ecosystem Summit (CDES) AT TopGolf

The Quiet Shift from Human to Autonomous AI Hacking. Are you ready to defend tomorrow?

On Sept 24 in Edison New Jersey at our regional CDE meet-up, we will explore together with Cybersecurity professionals from New Jersey, New York, and Pennsylvania. You are invited to join other local stakeholders to collaborate and combat cybercrime in the AI era.

The event brings together CISOs, CIOs, MSPs, MSSPs, and SOCs to foster essential teamwork to better protect businesses. Beyond the one-day meetup, members can build their own networks, join local chapters to meet/collaborate anytime and access some awesome free benefits from the CDE resource, including next generation cybersecurity insurance (you need to experience this for yourself to know why) and on-demand vCISO services or posture assessments so you can know the truth about the shape of your cybersecurity.

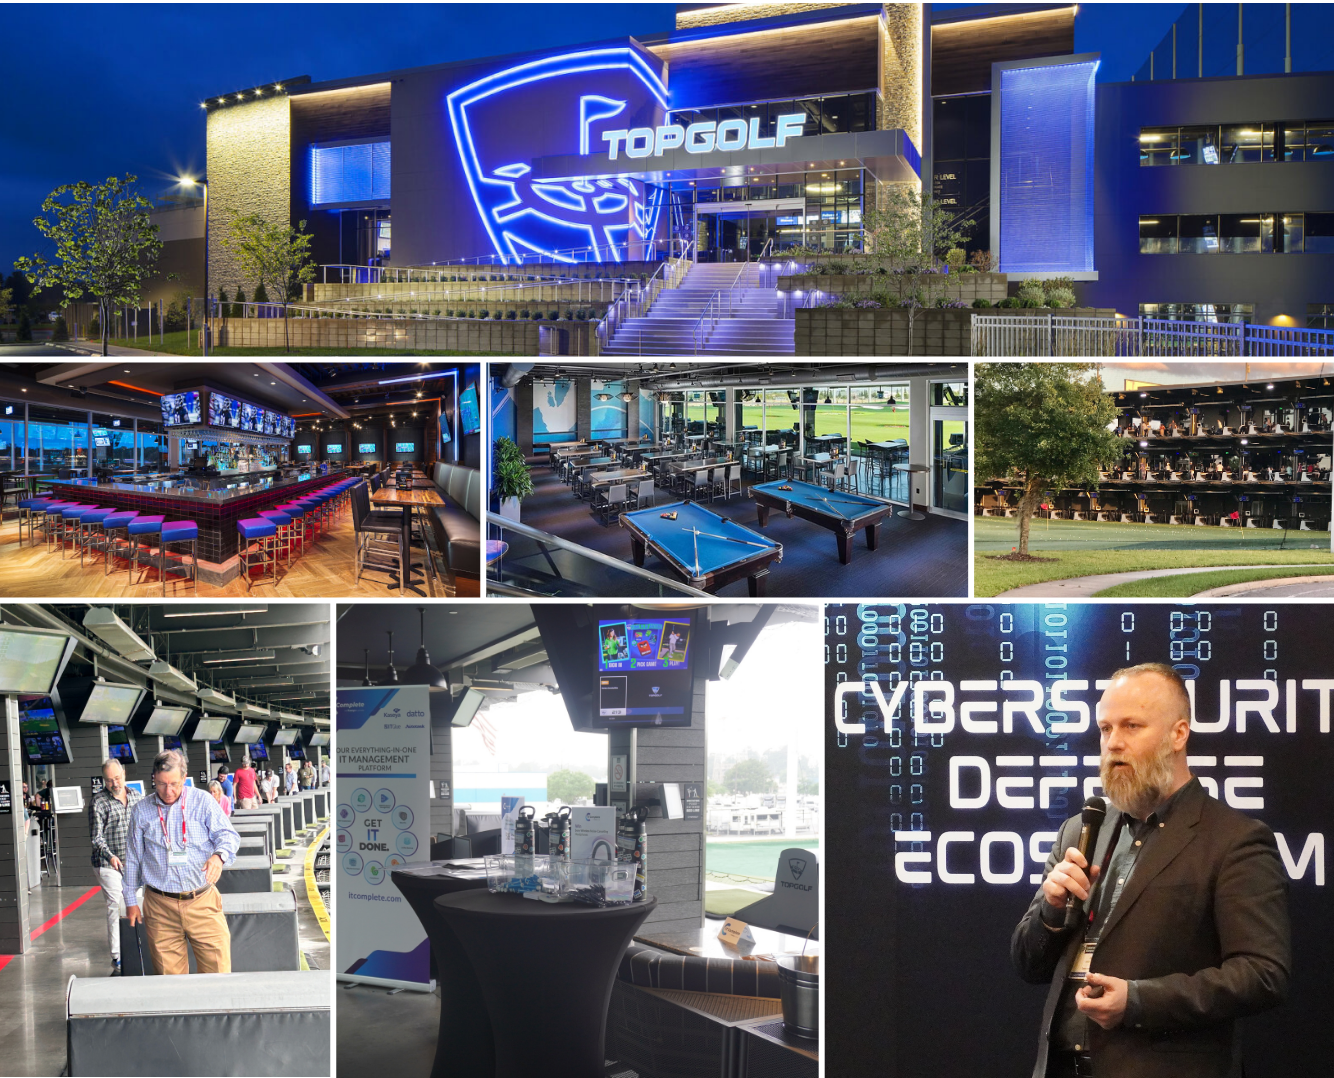
The Cybersecurity Defense Ecosystem Summit (CDES) will happen at the TopGolf in Edison, NJ on September 24.

It kicks off with a networking breakfast. The morning features dual educational tracks: “Left of Boom,” which analyzes how to defend against autonomous AI agentic hacking through continuous monitoring, tool consolidation, and smarter configuration strategies; and “Right of Boom,” which focuses on active incident response, real-time breach visibility, regular tabletop exercises, and securing affordable cyber insurance.

At 12:30 PM, the event transitions to the TopGolf bays for an afternoon of food, drinks, and casual social networking open to all skill levels.

By 2:00 PM, you can head home or choose your own adventure: continue picking the brains of cyber experts, participate in a peer-group mastermind session, or meet with investors actively looking to acquire cyber-first MSPs and MSSPs (explore what investors are looking for and what your company is worth).


You do not hear from these speakers often, but whenever you can, it’s well worth your time and attention. They don’t sell stuff. They are transferring vital knowledge that can help you every day. You want them to be in your network when the time comes. Impossible for you to not take home several brilliant ideas.

Attention Cyber Vendors: Learn how to build and nurture your partner sales pipeline from two experts in channel ecosystem.

This event is the local gathering of the Cybersecurity Defense Ecosystem Community Members and Non-Members! Click here to learn what is CDE!

Save $100 as your first CDE Free Member Benefit  for MSPs, MSSPs, SOCs and CISOs:

  • Days
  • Hours
  • Minutes
  • Seconds

CDE Video Overview

Event Details
Agenda Sept 24

Arrive by 8:30 AM to enjoy some breakfast snacks and coffee while networking with local cyber peers!

Your network is your net worth!

Welcome with a brief update on the latest CDE community benefits, now serving over 8,000 cyber-first members.

The Cybersecurity Defense Ecosystem is a dedicated community and resource for Cybersecurity-First MSPs, MSSPs, SOCs, and CISOs, focused on building resilient cybersecurity practice.

Leverage the resource with your free membership on demand. Explore the additional paid premium membership benefits.

These small regional summits serve as local meet-ups for our cybersecurity-first community (max 100 attendees) as well as potentially new members to network, learn, and explore resources to strengthen cyber posture and managed services.

Join a local chapter for year-round networking and learning opportunities.

Leverage a powerful resource of the CISO-approved cybersecurity solutions, tools, and related services - all year long.

CISOs and related cybersecurity professionals are welcomed to come learn and network with the channel community to help fulfill their cybersecurity mandates.

1. Meet, network and partner with local cyber peers and experts.
2. Learn the latest in cybersecurity
3. Find solutions to every cybersecurity challenge.
4. Leverage special tools and on-demand services like cybersecurity insurance, fractional vCISO services, security posture review and more.

The rapid rise of Autonomous AI Agentic hacking (now elevated with AGI) is fundamentally altering the security landscape as most experts know, and it is a fast-rising trend you cannot afford to underestimate.

It's simply getting too fast for humans only.

In this panel discussion of AI and Cyber experts, you will get the latest insights on how to best prepare and defend against AI with AI and humans in the loop.

One of our featured vendors can address the speed required to detect and mediate in real-time. Today, many vendors are shifting towards real-time interventions and increased predictability.

In this new AI environment, the speed at which we detect, mitigate, and recover from threats is absolutely mission-critical.

It is time to move beyond conventional cyber defenses. Embracing an AI-centric strategy that keeps humans in the loop is the only way to stay protected.

The industry is at a major turning point. Research firm Omdia notes that cybersecurity is currently facing shifts more significant than any seen in the last ten years, driven by the simultaneous convergence of platform consolidation, geopolitical shifts, AI transformation, and workforce disruption.

While everyone plays a part, the primary obstacles remain - cost and expertise, alongside evolving regulations like data sovereignty and compliance that are forcing a total rethink of strategy.

Managing the risks inherent in AI usage is also vital. The lack of a "delete" function in AI means that accidental data exposure is a persistent threat, with "Shadow AI" now joining as a major concern. As applications increasingly integrate AI, non-human entities like APIs are accessing and sharing data at an unprecedented scale. Furthermore, the deployment of Autonomous AI Agents—which can act and share information without direct user awareness—makes the control of these agents a mission-critical priority.

As businesses continue to adopt AI-powered solutions, it is paramount to establish strict governance and monitoring to counter risks such as AI poisoning, shadow AI, and improper employee usage.

AI has become a ubiquitous weapon for both attackers and defenders in the cyber war. Our objective is to construct a superior defense for the AI era by shifting from reactive tactics to predictive security and high-speed response. This means not just refining prioritization and reducing false positives, but fundamentally remaining ahead of the curve.

You will explore 7 questions that tell you whether your Cybersecurity Program actually works".

There's a lot of focus on tech stack and vulnerabilities, but how to actually know if your program is working from the business angle. This also helps get buy in from CEO, COO, CFOs as they don't understand the full cyber side.

Are you ready for this?

Gone are the good old days when the saying was "not if, but when you will be breached". Today it's how fast and how often will you be breached".

What will you do when the breach happens? You may be surprised to know what happens even by those who are well prepared.

Protecting yourself and your clients from cyber attacks has its limits, and a breach is highly probable despite best efforts. Even with frequent "cyber fire drills," most organizations remain unprepared for the reality of an intrusion.

The process is daunting: detecting the break, halting the breach, and investigating the timeline and methods used. You must then expel the attacker, verify the blast radius, and identify exactly which data was compromised, all while recovering systems, patching vulnerabilities, and addressing legal and PR consequences.

To help navigate these challenges, our "A-Team" of cybersecurity incident specialists DFIRs, CISOs, MSSPs and SOCs will offer essential insights into cutting-edge trends in breach detection, mediation, and recovery management. You will also hear unique perspectives from veteran Incident Response professionals.

If you are not ready for breach day, then you better know who to call to help save the day.

We will also include Compliance, Regulations and Cyber Insurance because these really matter after the breach! Defendable legal issues play a critical role in your cybersecurity posture.

Today, it's vital to keep ahead of the latest government and insurance regulations (both in-country and international). How do you get into compliance and stay compliant moving forward, and be able to prove it in case you have to in court or facilitate a claim with your insurance provider.

These experts will be available to answer your questions during our Mastermind Peer-Group sessions.

Security service providers don't need more vendor options—they need better-fitting ones. Chasing every compelling pitch spreads capacity thin across too many relationships, mastering none. The alternative is a disciplined framework for evaluating vendors on fit, quality, room to add value, marketability, ecosystem strength, and how crowded the field really is. Larry Walsh, Chief Analyst at Channelnomics, will provide guidance on how MSSPs should assess their security vendors.

Catch 2-minute pitches on cyber innovative solutions.
You'll get a high-level overview of select solutions and business tools, then vote for your favourite pitch.

Identify the vendors and tools that best fit your needs, and meet them later in the afternoon at their golf bay to dive deeper.

Vendors will be at their private golf bays, so you can meet, explore opportunities and potentially become a partner.

We will also highlight the afternoon session for MSPs and MSSPs looking to build valuations for an exit or to increase profitability. We will also explain how the Investor Matchmaking will work.

What's on YOUR mind? The session will feature an open mic discussion where the entire audience can engage and ask questions about the business of cybersecurity.

Join the exhibitors and speakers who will be hosting their exclusive golf-bay area to meet and play fun golf games. Everyone welcome. Drinks and food will be available.

Every MSP owner eventually asks the same questions: what is my business actually worth, who would buy it and, when will I be ready to sell?

This session is hosted by Michael Contentio, a leading MSP business valuation coach, author, previous MSP Owner and seasoned financial investor who has acquired many cyber-first MSPs and MSSPs.

You will learn what drives valuation, what earns a higher multiple, and what makes a deal fall apart in diligence. Bring your questions.

After this session, you can meet active investors to explore the opportunity. Meet one-on-one or in smaller groups. Whether you are thinking about selling next year or in ten years, the relationship starts with a conversation.

Come prepared: Complete your free MSP profile, and run the 15-Seconds valuation to find out what your MSP is worth ($79 for attendees, normally $295). Bring both printouts. The MSPs who stand out are the ones who arrive with their numbers organized.

Meet Paul Daigle, creator of the MSP Business Evaluator and the MSP Business Growth Marketplace. Paul built, scaled, and sold his own MSP, has advised on more than 700 M and A transactions, and manages over $1 billion in assets.

1. Your MSP profile (free): https://bizadvisoryboard.com/mspwellmatched_seller_questionnaire/

2. Recommended - Your valuation report ($79, normally $295, code CDESVAL73): https://bizadvisoryboard.com/msp-business-valuation/ How Much Is Your MSP Worth?

Investors will ask what your business is worth. Have the answer, and the numbers behind it.

Going further: the MSP Business Evaluator; Accelerator is the full diagnostic across all 8 Operational Focus Areas. It shows you where you stand against your peers and what to fix to raise your value. 10% off with code CDESACC10 (up to $995 off depending on version): https://bizadvisoryboard.com/msp-business-valuation/

Free: the $100M MSP Scaling Roadmap, three versions (Performance, Sales & Marketing, Human Resources). 100% off with code CDESROAD100: https://bizadvisoryboard.com/shop/

For those who want more, you have an option to participate in any of 3 Mastermind Peer-Groups whereby you collaborate with your peers to solve and a subject matter expert on your pain points.

1. Building Valuation to Exit Your MSP at The Maximum Multiple - Michael Contento

2. Talk with CISO - Adam Bennett

3. Tackling any Business Pain Point. The group members will choose which topic to tackle - Randal Wark

4. For Vendors only: Building you channel pipeline - Julian Lee and Larry Walsh

If you do not know what a Mastermind Peer-Group is about check out https://www.channelpartneralliance.com/#home

Even after the event officially concludes, the conversations usually continue. We often head out for dinner or gather at the bar to keep the discussions going in a more relaxed setting.

Registration
$195 CDE Members ($295 Non-Members)
295

Includes:

Full day access to the event
Breakfast
Lunch
Drinks
TopGolf Games
Parking

Topics on the short list to tackle:

1. Cybersecurity in the Age of AI Agents
A short opening talk framing how cybersecurity has shifted from AI awareness to AI execution, with AI agents, identity, data access, and automation now becoming real operational risks.

2. Frameworks
A practical discussion on how organizations should choose and apply frameworks without turning cybersecurity into checkbox compliance.

3. Vulnerability Prioritization in the Era of AI
What vulnerability prioritization actually means, why CVSS alone is not enough, and how teams should decide what to fix first.

4. Defense in Depth in the Era of AI
A modern look at layered defense across identity, email, endpoint, cloud, SaaS, data, AI agents, backups, and human behavior.

5. AI Pen Testing Lessons Learned
What breaks when testing AI applications, copilots, RAG systems, chatbots, and internal AI agents, and what organizations can do before production use.

6. The Rise of the CISO: AI Governance, Risk, and Board Communication
How security leaders explain AI risk, cyber investment, resilience, and business impact to executives and boards.

7. From Reactive to Predictive to Agentic Defense
A continuation of the AI defense conversation, moving from reactive security to predictive detection and safe AI-assisted response.

8. Identity Is No Longer Just About People
Human users, service accounts, APIs, bots, non-human identities, and AI agents that now need stronger governance and access control.

9. Shadow AI and Data Leakage
How employees are already using AI tools, where sensitive data may be leaking, and how companies can manage it without blocking innovation.

10. Ransomware 2026: Faster, Smarter, More Automated
A threat landscape update focused on ransomware, identity abuse, social engineering, and the operational gaps attackers continue to exploit.

11. Software Supply Chain and Third-Party Risk
How organizations can understand exposure across vendors, software components, SaaS tools, and critical third parties.

12. Cyber Insurance, Compliance, and Contracts
How cyber maturity now affects insurance, customer trust, procurement, and contract requirements.

13. Security Awareness in the Age of Deepfakes and AI Phishing
How awareness training must evolve when attackers can generate better phishing, voice cloning, deepfakes, and personalized scams.

14. Cyber Resilience: Recovery Is the New Differentiator
Backups, incident response, tabletop exercises, business continuity, and proving the organization can recover after an attack.

15. Vendor Proof, Not Vendor Promises
A sharper vendor pitch format where each vendor must explain the risk they solve, the proof they have, and the business outcome they deliver.

16. CISO Court: Put the Security Claim on Trial
The CISOs challenge on vendor claim, framework idea, or security assumption to test what is real, useful, and measurable.

17. AI Governance for MSPs and MSSPs
How MSPs and MSSPs can help customers adopt AI securely and turn AI security into a service opportunity.

18. What Can Be Done Now: 30/60/90-Day Cyber Action Plan
A closing action plan where experts give clear actions attendees can take immediately, within 60 days, and within 90 days.

FAQ

How do I become a Member to the Cybersecurity Defense Ecosystem (CDE) for FREE? It's simply - sign up at https://cybersecuritydefenseecosystem.com/channel-partner-sign-up/ .

When should I arrive? We start sharp at 9 AM, so please plan to arrive by 8:30 AM to meet everyone with some breakfast snacks and coffee.

Where do I park? Parking is in front of the complex and FREE.

Do I need to be a good golf player to participate in the games? NO! Whether you’re an aspiring golf pro or picking up a club for the first time, Topgolf is fun for all. And it’s a unique way to share fun time with business friends and partners in a very non-corporate setting. Ditch the boring stuffy conference rooms. Corporate team building events at Topgolf are like nowhere else.

Gallery

For some pictures from previous CDE Summits https://tpievents.smugmug.com/2025CDESummitToronto

Photos
Event Details
Sponsors
Share on social media